European Union opens door for Canada to become its first associate member
Prime Minister Mark Carney said Canada was seeking a ’unique alliance’ with the EU – but not membership

Prime Minister Mark Carney said Canada was seeking a ’unique alliance’ with the EU – but not membership
CVE-2026-87886 is a high-severity insecure file permissions flaw that can lead to local privilege escalation. The post Acronis Patches Exploited Vulnerability in cPanel Backup Plugin appeared first on SecurityWeek.
Microsoft has reminded customers that Windows Server 2022 will reach the end of mainstream support next month and enter extended support until October 2031. [...]
The security updates resolve over 800 vulnerabilities across 17 product families, including over 100 critical-severity flaws. The post Oracle Patches 800+ Vulnerabilities in September 2026 Security Update appeared first on SecurityWeek.
The vulnerability, tracked as CVE-2026-5430, can be exploited to gain access to valuable enterprise data. The post Enterprises Warned of Attacks Exploiting WSO2 Vulnerability appeared first on SecurityWeek.
Google has released the September 2026 security patches to address 110 vulnerabilities affecting its Pixel devices, including one zero-day flaw actively exploited in targeted attacks. [...]
A critical security flaw in WSO2 API Manager has come under active exploitation in the wild, according to findings from watchTowr. The vulnerability, tracked as CVE-2026-5430 (CVSS score: 9.8/10.0), is a case of improper verification of a cryptographic signature that could result in account takeover. Hacktro…

Threat actors are exploiting a critical security flaw in WooCommerce Wholesale Lead Capture, a premium WordPress plugin that has more than 6,000 active installs. "This vulnerability can be leveraged by unauthenticated attackers to upload arbitrary files, including PHP backdoors, and achieve remote code execu…

No summary available.
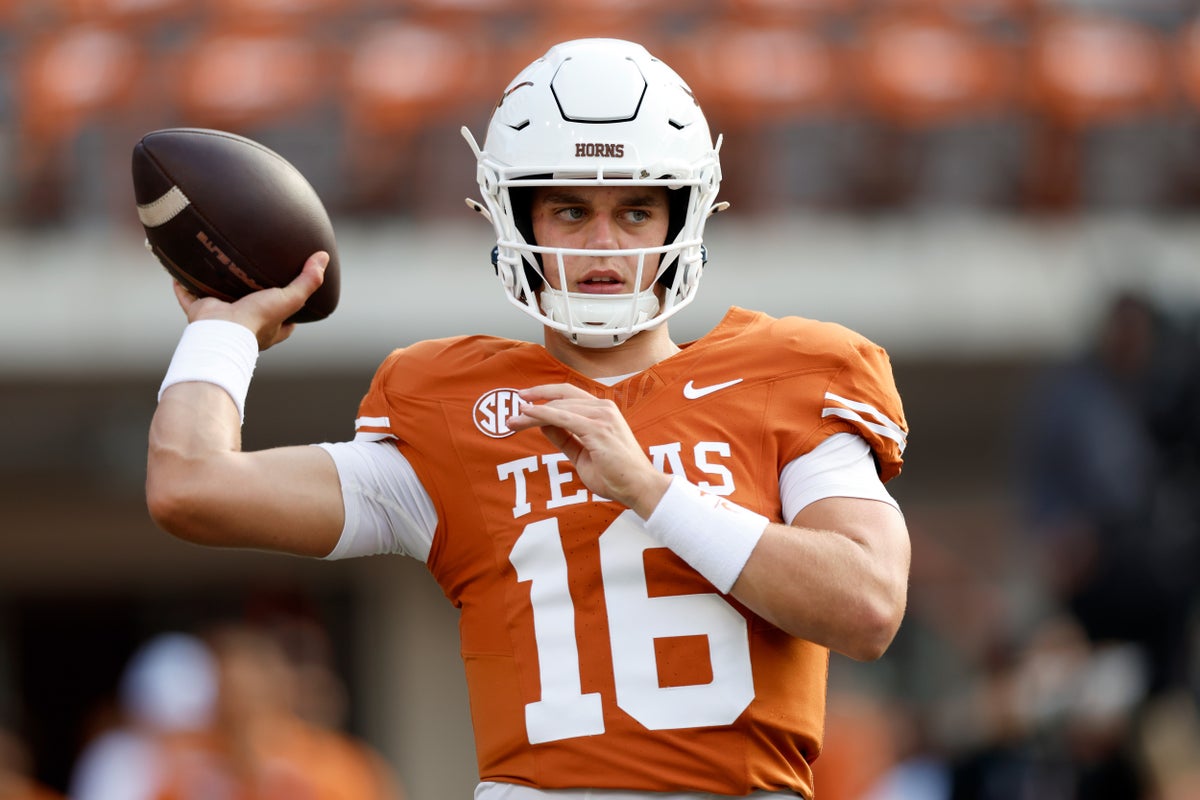
The fabricated footage parodied a post-game interaction following Texas’ 24-23 comeback victory over Ohio State on Saturday
A likely North Korean advanced persistent threat (APT) group used a previously undocumented Linux espionage toolkit to compromise load balancers, gain access to communications, and further exploit networks.
Acronis disclosed a high-severity Linux local privilege escalation vulnerability in its backup plugin for cPanel, WebHost Manager (WHM), and Plesk that may be exploited in the wild. [...]

You can't make an omelet without breaking a few eggs, and you can't patch nearly 1,000 CVEs without a few glitches.
Microsoft agreed to adopt guardrails and privacy standards for its AI in schools, as negotiated with the American Federation of Teachers. The post Microsoft Commits to Sweeping AI Privacy Rules for Students. Will Other Tech Giants Follow? appeared first on SecurityWeek.

Malicious versions of the Admin Menu Editor Pro plugin for WordPress have been distributed to more than 200 customers after a threat actor compromised the maintainer's website and pushed updates that created a hidden user account. [...]

The 'Breaking' News: The OpenAI–Hugging Face Incident - A Technical Reconstruction and Its Implications for AI At this Black Hat USA 2026 talk, OpenAI security engineers and researchers will reconstruct the OpenAI-Hugging Face incident and examine its implications for AI security, cyber resilience, and align…
Point-in-time audits and sampled assessments offer only snapshots; continuous control monitoring provides evidence that security controls are working today. The post “We Think the Security Control Is Working” Is No Longer Good Enough appeared first on SecurityWeek.
Cybersecurity researchers have shed light on a previously undocumented Brazilian banking malware operation that delivers a toolkit called KREMLIN. Elastic Security Labs is tracking the activity under the moniker REF9334. Active since at least May 2025, the threat actor has used lures that impersonate a dozen…

Cybersecurity agencies in the United States, the United Kingdom, and the Netherlands have detailed a Windows malware that they say Iran's intelligence service uses to spy on dissidents, journalists, and activists around the world. The malware is controlled via the Telegram messaging app and can copy a target…

The full-service malware-as-a-service (MaaS) platform offers a Windows implant, command-and-control (C2) infrastructure, and an operator panel for comprehensive remote access.
It was discovered that kitty incorrectly escaped error messages when handling specially crafted terminal escape sequences. A remote attacker could possibly use this issue to execute arbitrary commands. (CVE-2026-42850) It was discovered that kitty incorrectly handled remote edit requests in terminal output.…
It was discovered that SRT did not authenticate certain encryption control messages. A remote attacker could possibly use this issue to downgrade an encrypted connection and inject arbitrary content or interrupt a media stream. (CVE-2026-55868) It was discovered that SRT did not properly validate certain con…
Cédric Krier discovered that python-sql incorrectly escaped values passed to unary operators. An attacker could possibly use this issue to perform SQL injection attacks.
Guillem Lefait discovered that Suricata-Update did not properly validate destination paths when extracting files referenced by downloaded rule archives. An attacker could possibly use this issue to write arbitrary files outside the configured rules directory.
It was discovered that Snapcast incorrectly handled crafted JSON-RPC requests. A remote attacker could possibly use this issue to execute arbitrary code or obtain sensitive information.